Security
Identity and Access Management
Authentication
- The system uses JWT (JSON Web Token) for authentication
- Passwords are stored as bcrypt hashes -- never in plain text
- Configurable Session Timeout support (default: 4 weeks, recommended to reduce to 8 hours for production)
Single Sign-On (SSO)
The system supports integration with enterprise identity providers, configurable from the Admin Panel (26 settings fields):
- Microsoft Azure Active Directory (via OpenID Connect)
- Google Workspace
- Any SSO system supporting OAuth 2.0 / OpenID Connect
- LDAP (including Active Directory)
SSO Requirements
- SSO requires HTTPS -- Azure AD enforces
https://redirect URIs (except localhost). - SAML is not supported natively. Use a Keycloak intermediary to bridge SAML to OIDC if needed.
- When using LDAP with Active Directory, change the default attribute from
uidtosAMAccountName.
Role-Based Access Control (RBAC)
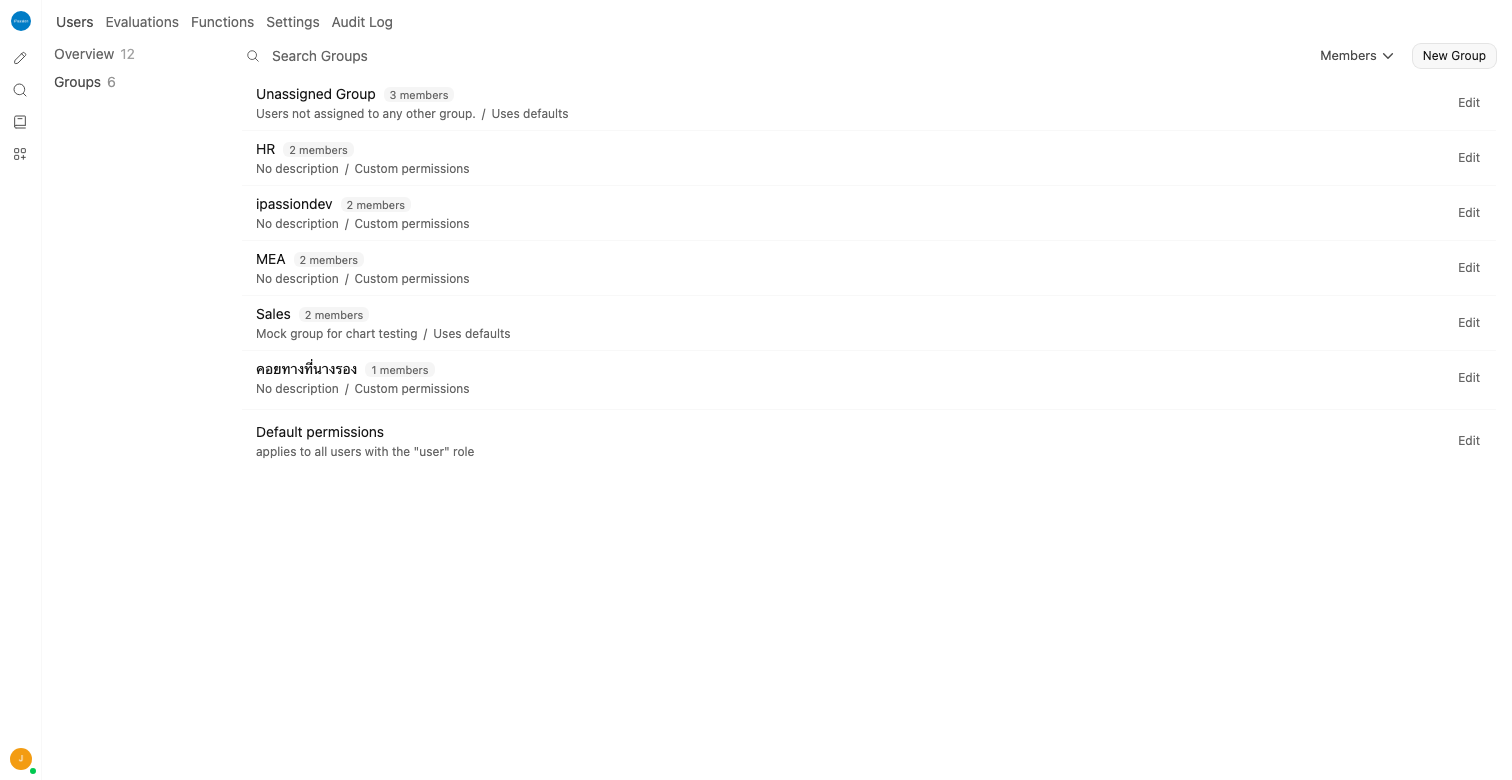
- Permissions assigned by role: Admin (ผู้ดูแลระบบ), Group Admin (ผู้ดูแลแผนก), User (ผู้ใช้), Pending (รอการอนุมัติ)
- Granular access control for: AI model usage, AI Agent creation, Knowledge Base management, Prompt Library management
- Group-level permissions can be customized per group or use system defaults
Data Protection
Encryption
- Data in Transit: HTTPS/TLS 1.2+ for all communications
- Data at Rest: Database encryption per PostgreSQL standards
Data Safeguards
- All data resides on organization-owned servers -- no external data storage
- Knowledge Bases have Access Control preventing unauthorized access
- Conversations are private to the owner only (unless explicitly shared)
PII Protection
- Built-in PII Guardrail filter function detects and blocks personally identifiable information (phone numbers, email addresses, Thai national ID numbers) in AI responses
Network Security
CORS (Cross-Origin Resource Sharing)
- Allowed origins are explicitly configured for API access
- Set via Environment Variable
CORS_ALLOW_ORIGIN
API Security
- All API endpoints require a Bearer Token
- Rate limiting to prevent abuse